Why Generic Appointment Software Fails Medical Spas: The Need for HIPAA-Compliant Systems
Key Takeaways
- Bookings are medical records: Connecting a client’s name to a clinical treatment creates sensitive protected health data.
- Generic software risks fines: Standard booking systems rarely sign legal privacy agreements, creating immediate compliance liabilities.
- Protection extends beyond scheduling: Intake forms, text alerts, patient photos, and staff permission settings all require legal privacy safeguards.
Why it matters: Medical spas often use standard salon scheduling tools. Because MedSpas handle clinical procedures, these generic tools trigger major legal privacy risks.
When Does Booking Data Become Sensitive Health Information?
The big picture: Protected health information includes any personal details tied to medical treatments stored or sent by a practice.
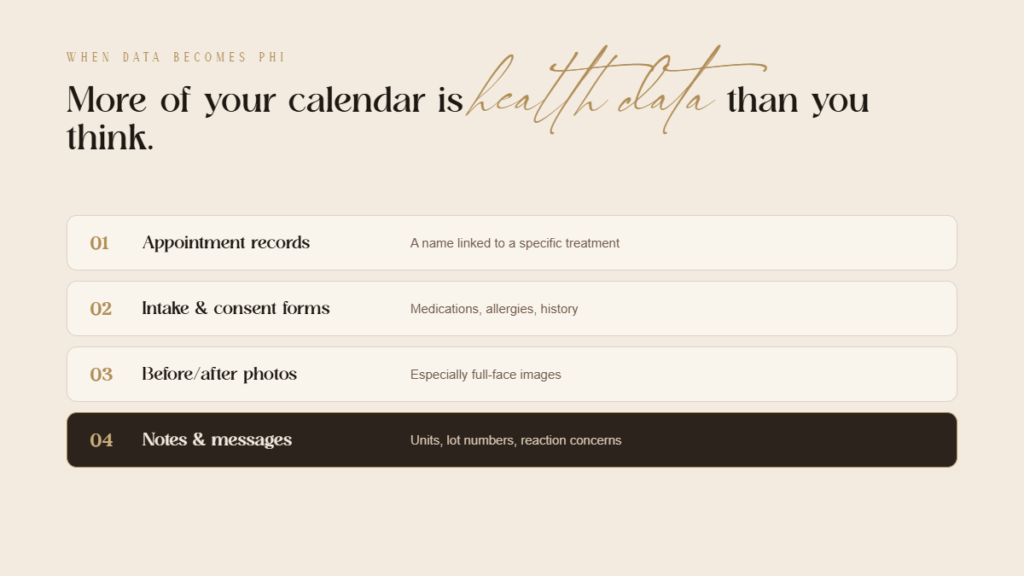
Common examples:
- Appointment records connecting a patient’s name to a specific procedure
- Intake forms detailing medications, allergies, health history, or pregnancy status
- Consent forms for specific procedures
- Client photos, particularly full-face treatment photos
- Treatment notes, dosage amounts, and product batch numbers
- Messages in which patients discuss reactions or concerns
Why Are Legal Vendor Contracts Essential?
The takeaway: Software providers handling patient data must sign a formal Business Associate Agreement (a mandatory legal privacy contract) to protect the business.
What the vendor contract requires:
- Binds vendors to follow strict federal health privacy standards
- Mandates prompt reporting of any data leaks or breaches
- Limits how the vendor can use and disclose patient data
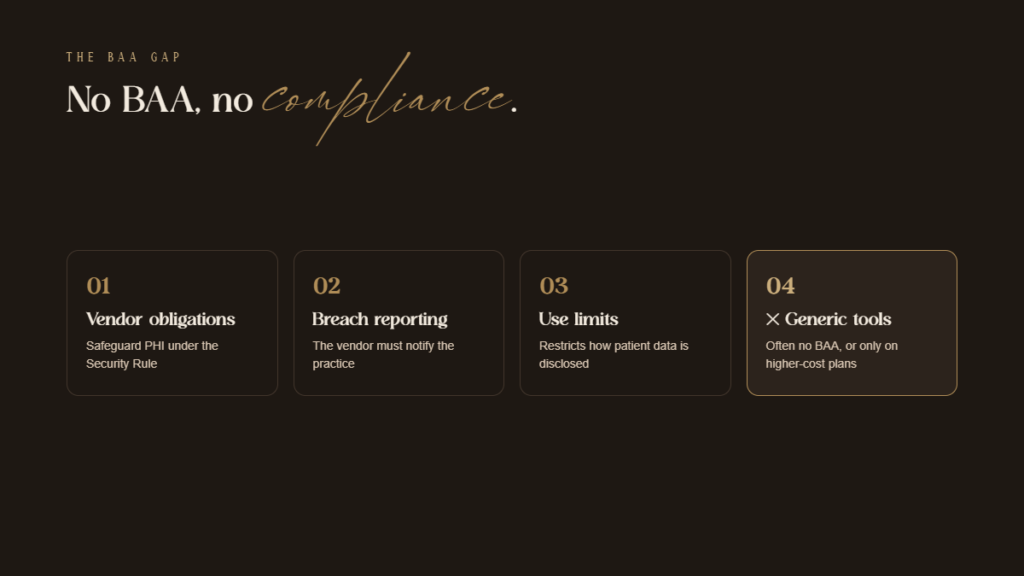
The issue: Generic scheduling software rarely offers these mandatory contracts, leaving medical spas open to regulatory fines.
Where Else Does Generic Software Fall Short?
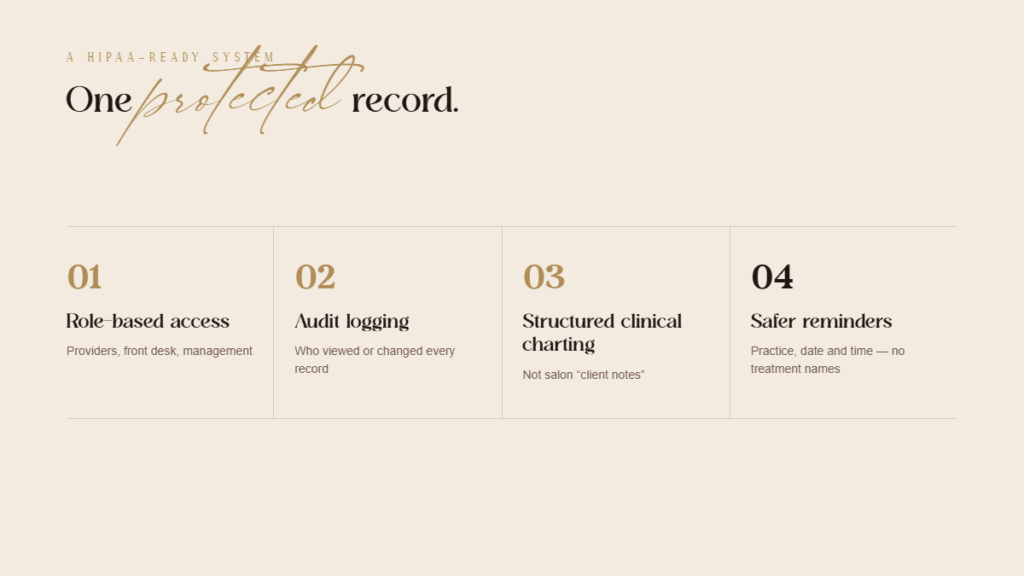
Staff access limits: Generic systems give all employees identical access, violating rules requiring role-based permissions.
Activity tracking: Standard software fails to track who opened or modified client files, missing mandatory security logs.
Audit logs: Generic apps rarely track who viewed or edited records, missing essential tracking required by the HIPAA Security Rule.
Data scrambling: MedSpas require secure encryption to scramble sensitive information in transit and in storage.
Clinical notes: Standard salon applications lack structure for logging dosages, lot numbers, settings, or digital signatures.
Clinical notes: Salon software lacks structure for tracking dosage, product lot numbers, device settings, or practitioner signatures.
Photo storage: Saving patient photos on unencrypted personal devices or shared drives exposes practices to major privacy breaches.
Are Appointment Reminders a Compliance Risk?
The bottom line: Text alerts are permissible, but message details must remain strictly minimal to safeguard client privacy.
Safer reminder practices:
- Use the practice name, date, and time without naming the treatment
- Avoid clinical details in SMS, which is generally not an encrypted channel
- Document patient communication preferences, including consent to receive texts
- Use compliant software backed by a signed privacy contract for messaging
What Are the Consequences of Getting It Wrong?
Severe penalties: Federal health privacy fines accumulate rapidly and can exceed $2 million annually.
Public disclosures: Data leaks mandate formal notifications to impacted clients, federal authorities, and potentially local news media.
Reputational loss: Privacy incidents destroy patient trust and damage practice reputation far beyond financial fines.
State laws: Local state privacy regulations create additional compliance risks alongside federal mandates.
What Features Does a MedSpa Platform Need?
- Signed vendor contract guaranteeing legal health privacy compliance
- Role-based access permissions tailored for clinicians, receptionists, and management
- Automatic activity tracking to log who views or updates records
- Data scrambling during transmission and storage
- Integrated clinical charting with structured treatment documentation
- Secure photo capture and storage within the patient record
- Digital intake and consent stored directly in the chart
- Secure two-way messaging with configurable reminder content
The Bottom Line
Why it matters: Generic tools are designed for hair salons, not medical practices. Operating without proper contracts, role permissions, or security tracking exposes MedSpas to immense liability.
Go deeper: Switching to a HIPAA-compliant platform combines appointments, chart notes, consents, and messaging into one secure workflow. Always consult legal counsel to review specific compliance requirements.
ready to grow & scale
more
about us
For brands looking for a branding, website and social media facelift...
The Aesthetic Website
learn more
For brands looking to SCALE & GROW their existing aesthetic business with more booked appointments...
The Aesthetic Accelerator
learn more
The client retention app for brands looking to maximize their client lifetime value and increase member retention
Juvvia
we are the creators of
REQUEST BETA ACCESS
follow us
chat with us
A data-driven performance marketing agency dedicated to helping aesthetic businesses scale and grow...
We Are LeadShark System
learn more